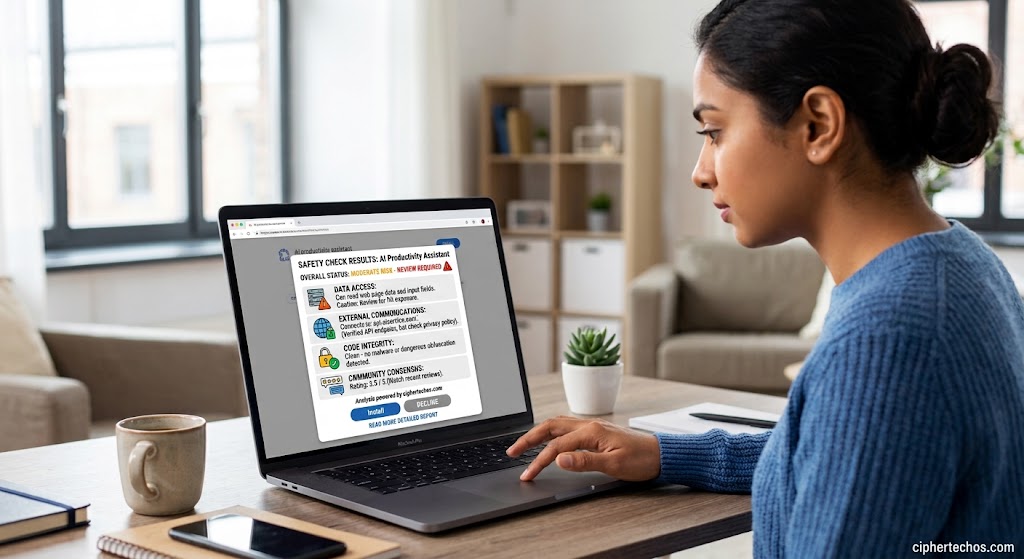
AI browser extension privacy is one of the most overlooked security topics of the past few years. Extensions that summarize pages, rewrite emails, translate text, and answer questions right inside your tab are convenient, and millions of people install them without a second thought. But to work, many of these tools need to read the pages you visit, and that raises a fair question: are AI extensions safe?
The honest answer is that some are, some aren’t, and the permission prompt you click through in two seconds won’t tell you which is which. This guide explains what AI extensions can actually see, the real risks (including ChatGPT Chrome extension risks like fake lookalikes), and a step-by-step process to vet any extension before you install it.
AI browser extensions can be safe when they come from a reputable publisher, request only the permissions they need, and handle your data transparently. The danger is not the category itself. It is that an extension sits between you and everything you do online, so a bad one is unusually costly.
How AI Browser Extensions Work
A browser extension is a small program that runs inside your browser and can modify how websites look and behave. Extensions are built with ordinary web technologies, and they can inject code into the pages you visit, add buttons and sidebars, and talk to remote servers.
AI extensions add one more ingredient: a connection to a large language model. Typically the flow looks like this:
- You open a page, or highlight some text, or click the extension’s button.
- The extension reads the relevant content from the page.
- It sends that content, often along with your instructions, to a server.
- A language model processes it and returns a result, such as a summary, translation, or draft reply.
- The extension displays the result in your browser.
Step 3 is where most privacy questions begin. The AI model usually does not run on your computer. Your content travels to someone’s server, and what happens there depends on the company, its policies, and its security practices. This is the core of AI browser extension privacy: you are not only trusting software on your device, you are trusting a chain of companies behind it.
What an AI Extension Can See
When you install an extension, the browser shows a permission prompt. The most common and most powerful one reads something like “Read and change all your data on all websites.” That wording sounds alarming, and it should get your attention. It is also how many legitimate extensions work, because an extension that summarizes any page needs access to any page.
An extension holding broad permissions can potentially access:
- The text of pages you open. That includes webmail, social media messages, banking dashboards, patient portals, and internal company tools.
- What you type. Search queries, form entries, comments, and chat messages can all be visible to code running on the page.
- Session data and cookies. On sites where you are logged in, an extension with the right permission may be able to read the tokens that keep you signed in.
- Your browsing activity. With the tabs and history permissions, an extension can see which sites you visit and when.
- Clipboard contents and downloads. Some extensions request these for features like “paste and rewrite” or “save as file.”
A well-behaved extension uses this access narrowly: it reads the page only when you ask, sends only what it needs, and does not store more than necessary. A careless or malicious one can quietly send the same information to a server you have never heard of.
One important point: permissions describe what an extension can do, not what it does do. You usually cannot see the difference from the outside. That is why vetting the publisher and the privacy practices matters as much as reading the permission list.
Are AI Extensions Safe? The Main Privacy Risks
If you are asking whether AI extensions are safe, these are the risks that matter most.
1. Your page content is sent to third parties
To summarize an article or draft a reply, the extension has to send text to an AI provider. That is normal, but it means anything on the page can leave your device. If you use the extension while viewing a client contract, a medical record, a private email thread, or an unreleased product document, that content is now in someone else’s systems.
Questions to ask about any extension:
- Who receives my data: the extension developer, an AI provider, or both?
- How long is it stored?
- Is it used to train or improve AI models?
- Can I delete it?
Many extensions answer these questions in a privacy policy. Some do not answer them at all.
2. Fake and copycat extensions
Popular AI brands attract imitators. Browser stores have, on multiple occasions, hosted extensions that borrowed the name and logo of well-known AI tools while doing something very different, such as stealing session cookies or injecting ads. Store search results can make a lookalike appear right next to the real thing, and a name that sounds official is not proof of anything.
The safest habit is to avoid searching the store for the tool. Instead, go to the AI provider’s own website and follow its link to the official extension.
3. Extensions that change hands or get compromised
An extension you vetted a year ago may not be the same extension today. Developers sometimes sell popular extensions to new owners, and attackers sometimes compromise a developer’s account and push a malicious update. Because browsers update extensions automatically in the background, you may never see a notice that anything changed.
This is why a one-time review is not enough, and why regular audits (covered below) are worth the few minutes they take.
4. Data collection hidden in the fine print
Some free extensions, particularly “AI assistant” add-ons, free VPN-style tools, and productivity helpers, have been reported to collect browsing data or even the content of AI conversations and then share or sell it. The business model is not always visible. A useful rule: if the product is free, has no obvious revenue source, and asks for broad permissions, ask how it pays its bills. If the answer is not clear, your data may be the product.
5. Overbroad permissions
An extension that only needs to work on one site but requests access to all sites is a red flag. So is a writing helper that asks for your browsing history or a summarizer that wants access to your downloads. Every extra permission increases the damage if the extension is ever misused, hacked, or sold.
6. Prompt injection through web pages
This risk is newer and specific to AI. When an extension feeds page content into a language model, the page itself can contain hidden instructions written to manipulate the AI, such as text telling the model to ignore your request and do something else. If the extension can take actions (send messages, fill forms, navigate), a manipulated model could be steered into doing things you never asked for. Extensions that only read and summarize carry less of this risk than “agent”-style extensions that act on your behalf. The more autonomy an extension has, the more carefully you should evaluate it.
7. Weak security on the developer’s side
Even an honest developer can be a weak link. If the extension sends your data to a backend with poor security, a breach at the developer’s end exposes everything users sent. Small teams and solo developers may not have the resources for strong security practices, and that is hard to judge from the outside, which is why transparency signals such as published security contacts and audits are worth looking for.
ChatGPT Chrome Extension Risks
“ChatGPT” is one of the most searched AI terms, which makes it one of the most abused names in browser stores. Here is how ChatGPT Chrome extension risks typically show up.
Lookalike branding. Many extensions use “ChatGPT” in their name or icon without being made by OpenAI. Some are legitimate third-party tools that add a sidebar or shortcut for the service. Others exist to harvest data. The name alone cannot tell you which.
Login and session exposure. Some third-party extensions ask you to log in to your AI account through them, or they sit on the page where you are already logged in. If an extension can read your session data, a malicious one could potentially take over the account, view your conversation history, or use your paid plan.
Conversation history exposure. People often paste sensitive things into AI chats: work documents, personal problems, code, even credentials. An extension with access to the page can read those conversations as they happen. This is a good reason to think twice about running unrelated extensions on the AI chat site itself.
Unofficial “free access” promises. Be especially skeptical of extensions promising free premium features, unlimited usage, or “unlocked” models. These promises are a classic lure for malware and data harvesting.
How to reduce the risk:
- Get extensions only through links on the AI provider’s official site.
- Check that the publisher name matches the company you expect.
- Never enter your AI account password into an extension’s own window.
- Use a separate browser profile with minimal extensions for AI chat sessions that involve sensitive material.
The same logic applies to every other AI brand. Imitators follow popularity, so a growing AI tool is a likely target for copycats.
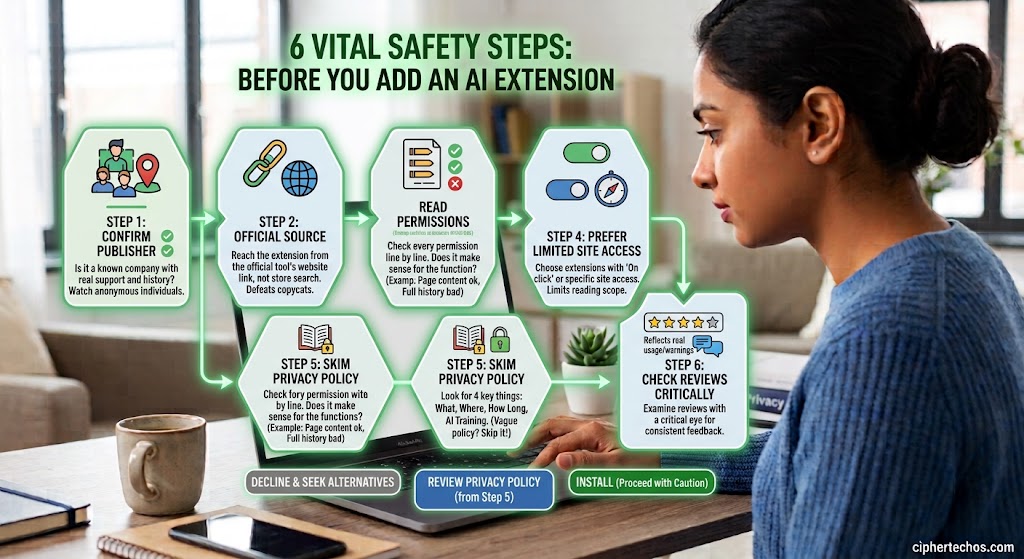
How to Vet an AI Extension: A 10-Step Checklist
Run through these steps before you click “Add to Chrome” (or the equivalent in your browser). The whole process takes about five minutes.
Step 1: Confirm who made it
Look at the publisher name and the developer’s website. Is it a known company with a real address, support team, and history? Or is it an anonymous individual with a generic email and no track record? Be most cautious with unknown publishers asking for broad permissions.
Step 2: Reach the extension through the official source
If the extension claims to belong to a known AI tool, find the link on that tool’s official website rather than searching the store. This single step defeats most copycat attempts.
Step 3: Read the permission list line by line
Click the permissions or “Privacy practices” section in the store listing. Ask whether each permission makes sense for the advertised function. A page summarizer reading page content is reasonable. A page summarizer wanting your full browsing history is not.
Step 4: Prefer limited site access
Where possible, choose extensions that work only on click or only on specific sites. In Chrome, you can open the extension’s details and set site access to “On click” or “On specific sites.” This limits what the extension can read at any given time.
Step 5: Skim the privacy policy for four things
You do not need to read every word. Look for:
- What is collected: page content, prompts, browsing data, device information.
- Where it goes: the developer’s servers, a named AI provider, other third parties.
- How long it is kept: a clear retention period is a good sign.
- Whether it trains AI models: and whether you can opt out.
If there is no privacy policy, or it is vague and full of broad language about sharing with “partners,” treat that as a reason to skip the extension.
Step 6: Check reviews with a critical eye
Read recent reviews rather than relying on the star average. Look for mentions of unexpected ads, hijacked searches, new permission requests after an update, or strange behavior. Be suspicious of a sudden burst of five-star reviews with generic wording, or an extension with few users but glowing praise.
Step 7: Look at update history and ownership
Check when the extension was last updated and whether the developer changed recently. An extension with no updates for years may be abandoned and vulnerable. One that recently changed hands deserves a fresh look at its permissions and policy.
Step 8: Look for transparency signals
Positive signs include open-source code, a published security contact or vulnerability disclosure process, independent security audits, and a clear explanation of how the product makes money. None of these is a guarantee, but each counts in the extension’s favor.
Step 9: Test in a separate browser profile
Create a fresh browser profile with no logged-in accounts, install the extension there, and try it for a few days. Watch for odd behavior, extra permission prompts, or unexpected network activity. Keep banking, health, and work accounts out of that profile.
Step 10: Set a review date
Put a reminder in your calendar to re-check the extension in three months. Policies change, ownership changes, and updates change behavior. A quick re-check keeps an old decision from becoming a stale one.
Red Flags at a Glance
| Red flag | Why it matters |
| Anonymous developer, no website | No accountability if something goes wrong |
| Requests access to all sites for a narrow task | More exposure than the feature needs |
| No privacy policy or a vague one | You cannot know how your data is handled |
| Promises of free premium AI access | Common lure for data harvesting and malware |
| Name and icon closely mimic a famous brand | Possible impersonation |
| Sudden new permissions after an update | Behavior may have changed |
| Burst of generic five-star reviews | Possible fake review campaign |
| Asks for your AI account password directly | Credential theft risk |
| Developer recently changed with no explanation | Ownership change can mean new motives |
If an extension shows more than one of these, skip it.
Habits That Reduce Your Risk
Vetting handles the moment of installation. These habits handle everything after.
Install fewer extensions. Each one is additional attack surface. If you have not used an extension in a month, remove it.
Restrict site access. Use “on click” or “specific sites” settings so an extension cannot read pages you did not intend to share with it.
Keep sensitive work in a clean profile. Use a dedicated browser profile with no AI extensions for banking, healthcare, legal, and confidential work. Profiles keep extensions, cookies, and logins separated.
Do not paste secrets into AI tools. Passwords, API keys, financial account numbers, and personal identifiers do not belong in any prompt, whether in an extension or a chat window. If you would not email it to a stranger, do not feed it to a third-party tool.
Turn off history and training where you can. Many AI services offer settings to limit data retention or opt out of model training. Using them reduces the long-term footprint of anything you do share.
Audit regularly. Every few months, open your browser’s extension page and go through each item. Remove anything unfamiliar, unused, or recently changed. This is the habit most likely to catch an extension that has quietly turned bad.
Keep your browser updated. Browser updates patch security holes that malicious extensions might exploit.
Use the browser’s own features first. Many browsers now include built-in summarizing, translating, and reading tools. These live inside the browser vendor’s own security model and may not require adding a new third party to your trust chain. They are not risk-free, but they reduce the number of companies handling your data.
AI Extensions at Work: What Teams Should Know
If you use a work computer or handle company data, the stakes rise.
Check your policy first. Many organizations restrict or prohibit AI extensions because of data-leak concerns. Installing one without approval could violate company policy even if the extension itself is harmless.
Understand what is exposed. Internal tools, customer records, unreleased plans, and source code are all visible to an extension running on those pages. Sending any of it to an external AI provider may breach confidentiality agreements or regulations.
Use managed options. Businesses can often manage extensions centrally, allowing only approved ones and blocking the rest. If your company offers an approved AI tool with a proper data agreement, use that instead of a personal extension.
Think about regulated data. Healthcare, finance, legal, and education settings often carry specific rules about where data can go. An AI extension that sends content to an outside server may not meet those requirements.
Ask the question before you install. A short message to your IT or security team is a lot cheaper than an incident report.
For teams building a policy, an approved-extensions list, a short review process, and a clear rule about what data can be entered into AI tools will cover most of the risk. [INTERNAL LINK: AI usage policy template or workplace data security post]
What to Do If You Installed a Bad Extension
If an extension behaves strangely, or you realize you installed something shady, act quickly.
- Remove it. Open your browser’s extension page and uninstall it.
- Change passwords. Start with email, banking, and any account you used while the extension was installed, and use a different device if you suspect your computer is compromised.
- Sign out of active sessions. Many services let you log out of all devices, which invalidates any stolen session tokens.
- Turn on two-factor authentication. If you have not already, enable it on important accounts.
- Scan your device. Run a reputable security scan to check for other unwanted software.
- Check for unusual activity. Review recent logins, sent messages, and financial transactions for anything you did not do.
- Report the extension. Use the store’s report option so others are protected.
- Tell your employer if it was a work device. Prompt disclosure helps security teams contain any damage.
Do not wait for proof that something happened. If an extension looked suspicious, treat it as compromised and clean up.
Safer Alternatives to Always-On Extensions
You do not have to choose between using AI and protecting your privacy. Some lower-exposure options:
- Use the AI provider’s website or app directly. Copying text into the official site means you choose exactly what is shared, and nothing reads your pages in the background.
- Use extensions only on click. An extension that reads a page only when you press its button sees far less than one running everywhere.
- Choose built-in browser features. Native summarizing and translation tools reduce the number of third parties involved.
- Use a dedicated profile. Keep an “AI tools” profile separate from the one holding your logins.
- Pick tools with clear data commitments. Favor services that state plainly that they do not train on your content or that offer enterprise-grade data terms.
The aim is not to avoid every extension. It is to make sure each one earns its access.
Frequently Asked Questions
Are AI browser extensions safe to use?
They can be safe when they come from reputable publishers, request only the permissions they need, and have clear privacy policies. They are riskier when the developer is anonymous, the permissions are broad, or the data practices are unclear. Vet each extension individually rather than assuming the whole category is safe or unsafe.
Can an AI extension read my passwords or private messages?
With broad permissions, an extension can potentially read anything displayed on pages you visit, including private messages and form fields. It can also access session data on some sites. Whether it actually does so depends on the extension. This is why limiting site access and keeping sensitive accounts in a clean browser profile helps.
Is the ChatGPT Chrome extension safe?
It depends on which extension you mean. Many extensions use the ChatGPT name without being made by OpenAI. Some are harmless third-party tools, and others are designed to collect data. Always reach an extension through the AI provider’s official website, check the publisher name, and never enter your account password into an extension’s own window.
Do AI extensions use my data to train models?
Some do and some do not. It depends on the extension developer and the AI provider behind it. Check the privacy policy for a statement about training, and look for opt-out settings. If the policy does not address it, assume your content could be retained and used, and avoid sharing sensitive material.
How can I tell if an extension is a fake?
Check that the publisher matches the company you expect, reach it from the official site rather than a store search, and compare the user count and reviews to what you would expect for a well-known tool. Be wary of generic reviews, lookalike names, and promises of free premium access. If in doubt, do not install it.
Conclusion – Convenience Is Worth It Only If You Stay in Control
AI browser extensions are not inherently dangerous, and many are genuinely useful. But because they sit between you and everything you do online, the cost of a bad one is high, and the signs of a bad one are easy to miss.
The fix is simple and repeatable: confirm the publisher, reach the extension through the official source, read the permissions, skim the privacy policy, test in a separate profile, and re-check periodically. Combine that with a few habits, such as installing fewer extensions, limiting site access, keeping secrets out of prompts, and keeping sensitive work in a clean profile, and you can enjoy the convenience without handing over the keys to your browser.
Take five minutes to run through the checklist before you click “Add to Chrome.” It is far easier than cleaning up after a compromised account.