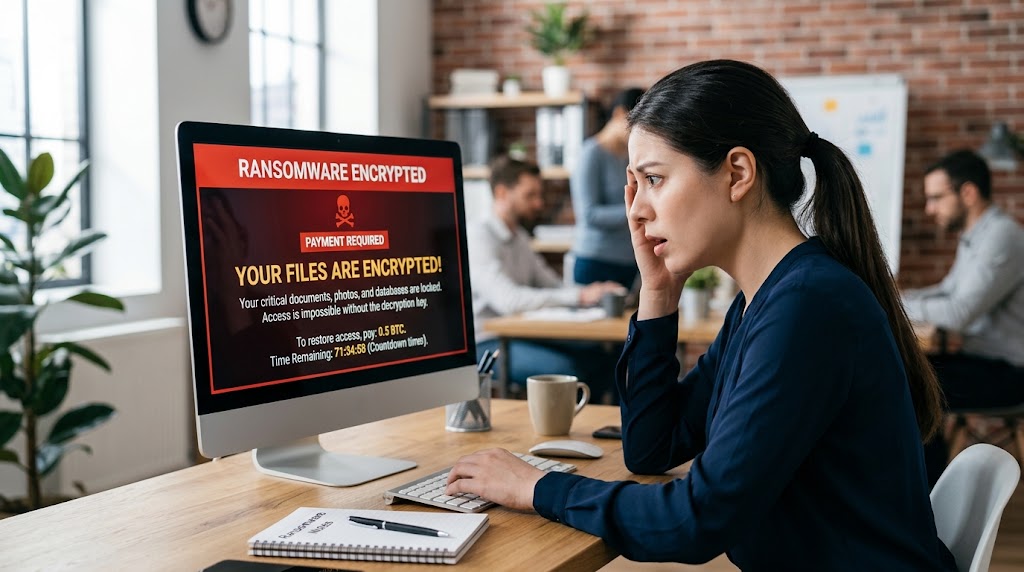
What is ransomware , how it gets in, and exactly what to do in the first hours of an attack. A practical guide for individuals and small businesses.
Ransomware attacks tend to start the same way: someone sits down at a computer, and their files won’t open. Documents have strange extensions. A text file or full-screen message says everything has been encrypted and tells them how to pay to get it back. The photos, the invoices, the thesis, the customer database are all still on the machine, but they’re locked, and somebody else holds the key.
If that has happened to you, skip ahead to the section on what to do in the first hour. If you’re reading this to prepare, which is a far better position to be in, the rest of the article explains how ransomware works, how it usually gets in, and how to make an attack survivable. Most of what protects you is unglamorous: backups, updates, strong logins, and a plan.
What ransomware is?
Ransomware is malicious software that blocks access to your data or systems and demands payment to restore it. The name says it all: a ransom, demanded for something taken hostage.
Most ransomware works by encryption. It scrambles your files using a cryptographic key that only the attacker holds. Without that key, the files are unreadable, and decent encryption can’t realistically be broken by brute force. A smaller group of attacks, sometimes called lockers, simply lock you out of the device or screen without encrypting individual files, which is often easier to undo.
The victims aren’t limited to big corporations. Individuals, schools, hospitals, local governments, small shops, and charities all get hit. Attackers go after whoever is easiest to breach and most likely to pay, and a small business with unpatched software and no tested backups fits that description better than a large company with a security team.
How an attack usually unfolds
It helps to understand that ransomware is rarely the first thing that happens. The encryption is the final act. Before that, attackers often spend days or weeks inside a network, which is why spotting early warning signs matters.
A typical sequence looks like this:
- Getting in. The attacker finds a way into a computer or account (more on this below).
- Settling in. They look around, find out what the network contains, and try to gain higher-level access, such as administrator accounts.
- Finding and disabling defenses. Backups, security tools, and monitoring are often targeted, because a victim with working backups doesn’t need to pay.
- Stealing data. Many modern attacks copy sensitive files out of the network before encrypting anything.
- Encrypting. Once they’re in a strong position, they launch the encryption across as many systems as possible, often at night or on a weekend when fewer people are watching.
- Demanding payment. A ransom note appears, usually with instructions for contacting the attackers and paying, most often in cryptocurrency.
Attacks against individuals are generally simpler and faster, but the core idea is the same.
Types of ransomware
You’ll see a few terms used in the news, and they’re worth knowing.
Crypto ransomware encrypts your files and demands payment for the decryption key. This is the most common type.
Locker ransomware locks you out of your device or its screen instead of scrambling the files. It’s more common on older or mobile systems, and often easier to recover from.
Double extortion adds a second threat. Attackers steal your data before encrypting it, then threaten to publish or sell it if you don’t pay. This matters because restoring from backups solves the encryption problem but not the leak. Even a victim with perfect backups can still be pressured.
Triple extortion goes further, adding pressure on your customers, partners, or patients, or threatening additional attacks such as denial-of-service floods.
Ransomware-as-a-service (RaaS) is a business model in which a core group builds and maintains the malware and rents it to affiliates who carry out the attacks, splitting the profits. This is a big reason the problem has grown: someone doesn’t need technical skill to run an attack anymore, only the willingness to use a ready-made kit.
How ransomware gets in
Understanding the common entry points tells you where to put your defenses. The same few methods account for a large share of incidents.
Phishing emails and messages. A message convinces someone to open an attachment, click a link, or enter their login on a fake page. It might look like an invoice, a delivery notice, a shared document, or a message from a boss. This remains one of the most common routes.
Stolen or weak credentials. Attackers buy leaked usernames and passwords, or guess weak ones, and log in like a normal user. If you reuse passwords across sites, one breach elsewhere can unlock your accounts here. Accounts without two-factor authentication are especially exposed.
Exposed remote access. Remote desktop and similar tools left open to the internet, with weak passwords, have been a long-running way in for attackers.
Unpatched software. Known vulnerabilities in operating systems, VPNs, firewalls, and business applications are exploited quickly after being published. Systems that haven’t received updates are easy targets.
Malicious downloads and ads. Pirated software, fake installers, cracked games, and “free” tools can carry malware. So can compromised or fake websites.
Infected USB drives and removable media. Less common now, but still possible, especially in workplaces.
Compromised vendors and software supply chains. Sometimes the way in is through a trusted supplier or a piece of software you rely on that has itself been breached.
If you notice, none of these requires a movie-style hacker. They exploit ordinary habits: a rushed click, an old password, a delayed update.
Warning signs of an attack in progress
Sometimes there’s a short window before the encryption finishes. If you notice any of these, act immediately rather than waiting to see what happens:
- Files suddenly changing names or extensions, or refusing to open
- A computer running unusually slowly, with the disk working hard for no reason
- Security software that has been switched off or can’t be reopened
- Unfamiliar programs or user accounts appearing
- Backup jobs failing, or backup files disappearing
- Messages from colleagues reporting the same strange behavior
- A ransom note appearing on one machine
Speed counts. Encryption spreads, and every minute you spend uncertain is a minute it may be reaching more files and more devices.
What to do if you’re hit: the first hour
This is the part most people need. The guidance below follows the general advice from government cybersecurity agencies and incident response professionals. For a business, it also reflects your own incident response plan if you have one. If you don’t, use this as a starting point.
1. Stay calm and don’t rush into paying
Panic leads to bad decisions, and attackers deliberately create pressure with countdown timers and threats. A deadline on a ransom note is a negotiation tactic. Take a breath. You have more options than the note suggests.
2. Isolate the affected devices immediately
Disconnect the infected computer from everything: unplug the network cable, turn off Wi-Fi, and disable Bluetooth. If it’s a business, take affected machines off the network quickly, and disconnect shared drives and servers if you suspect they’re affected. The aim is to stop the infection spreading to other devices and to stop the attacker communicating with it.
You may hear advice to shut the machine down entirely. Cutting the network is the priority. Whether to power off depends on the situation, because shutting down can destroy useful evidence held in memory, while leaving it running can allow encryption to continue. If you have IT or incident response support, ask them. If you don’t, disconnect first and don’t wipe or reinstall anything yet.
3. Protect your backups
Check right away whether your backups are intact and whether they’re connected to the compromised system. If a backup drive is plugged in, unplug it. If you use a network backup or cloud backup, don’t assume it’s safe. Check recent versions before the infection, and consider changing the credentials that access it, from a clean device.
This is where the 3-2-1 approach pays off: multiple copies, on different media, with at least one stored offline or offsite. If you’ve got a clean offline copy, your situation is dramatically better.
4. Don’t delete, wipe, or reinstall yet
It’s tempting to wipe the machine and start fresh. Don’t do it yet. The infected system, the ransom note, and any logs are evidence. They can help identify the type of ransomware, which can determine whether a free decryptor exists. They’re also useful to investigators and insurers. Photograph the ransom note with your phone, and keep any files the attackers mention, including email addresses, wallet addresses, or contact links.
5. Identify the ransomware
Knowing which variant you’re dealing with changes what’s possible. Services like ID Ransomware let you upload a sample of an encrypted file and the ransom note to help identify the strain. Do this from a clean device, not the infected one.
6. Check for a free decryptor
For some ransomware families, security researchers and law enforcement have recovered keys or found flaws that allow files to be decrypted without paying. The No More Ransom project, a collaboration between law enforcement and security companies, hosts free decryption tools and guidance. It won’t have a solution for every strain, and newer or professional variants are often not covered, but it costs nothing to check.
7. Change credentials, from a clean device
Assume the attacker may have captured passwords. Using a device you’re confident is clean, change passwords for email, banking, cloud storage, and any accounts that were logged in on the affected machine. Start with your email and administrator accounts, since they let attackers reset everything else. Turn on two-factor authentication wherever it’s missing. In a business, reset credentials for affected users, service accounts, and administrators, and revoke active sessions.
8. Tell the right people
Who you notify depends on whether you’re an individual or an organization.
Individuals: Report to your local police or national cybercrime reporting service. In the US, that’s the FBI’s Internet Crime Complaint Center (IC3). In the UK, it’s Action Fraud and the NCSC. Other countries have their own national cybercrime or computer emergency response team. Reports help investigators track criminal groups and sometimes lead to recovered decryption keys.
Businesses: Bring in your IT provider or an incident response firm if you have one. Notify your cyber insurance provider promptly, because many policies require quick notice and may provide response support, and acting without their involvement can sometimes complicate a claim. Contact law enforcement, and if you’re in the US, CISA also accepts incident reports. Consider talking to a lawyer early, since data breach notification rules may apply.
9. Work out the scope
Figure out which systems and data were affected. Which computers show the ransom note? Which shared folders are encrypted? Is there any sign data was copied out? In a business, this is a job for a professional investigator, because the attacker may still have access somewhere in the network even after the visible damage is contained.
10. Decide how to recover
Once the situation is contained, you have a few paths: restore from backups, use a free decryptor if one exists, rebuild affected systems, or, as a last resort, consider paying. The next two sections cover the last two in detail.
Should you pay the ransom?
Law enforcement agencies and security authorities generally advise against paying. That’s not just principle. There are practical reasons.
Payment doesn’t guarantee recovery. Some victims pay and receive no key. Others receive a decryptor that’s slow, buggy, or only partly works, leaving some files corrupted or unrecoverable.
It funds further crime. Payment finances the criminals’ next attacks and encourages the business model.
You can be targeted again. Paying can mark you as a victim who gives in. Some organizations have been attacked again after paying.
It doesn’t solve the data theft problem. If data was stolen, paying doesn’t prove it’s been deleted. The attackers can still keep or sell it.
There may be legal risk. In some jurisdictions, paying certain groups can violate sanctions or other laws, particularly if the attackers are linked to sanctioned entities. Reporting requirements for ransom payments are also emerging in various places. This is a legal question, not just an ethical one, so speak to a lawyer and your insurer before any payment.
All that said, people do face genuinely hard choices. A hospital might have lives at stake. A small business without backups might face closure. A family might have the only photos of a loved one who has died. These decisions are real, and no article can make them for you. If you’re in that position, get professional advice, understand the legal implications, and know that recovery after payment isn’t assured. Never pay without first checking whether a free decryptor exists and whether a clean backup can be restored.
Recovering after an attack
Recovery is more than getting the files back. If you restore data onto a system that’s still compromised, you may be hit again within days.
Rebuild or clean the affected systems. The safest approach is to wipe and reinstall the operating system on infected machines, rather than trying to clean them in place. Malware can hide in ways that are hard to confirm are gone.
Restore from a known-clean backup. Check that the backup predates the infection. If attackers were inside your network for weeks, recent backups may also contain malicious files. Scan restored data before connecting it to your network.
Patch everything. Whatever vulnerability let the attackers in must be closed before systems go back online. Update operating systems, applications, firmware, and anything else with outdated software.
Reset credentials thoroughly. Change passwords, revoke tokens, and review accounts for unfamiliar users or permissions. If attackers reached administrator-level accounts, reset those with extra care.
Bring systems back in stages. Reconnect critical systems first, watch for signs of reinfection, and then restore the rest.
Monitor afterwards. For weeks after, keep a close eye on logs and unusual activity. Attackers sometimes leave hidden access points to return later.
Deal with stolen data. If sensitive data was taken, you may have legal duties to notify affected people or regulators. Rules vary widely by country and industry, so get qualified advice. For individuals whose personal data may have been exposed, watching accounts for suspicious activity and considering a credit freeze where available can limit later harm.
Learn from it. Once things are stable, work out how it happened and what would have stopped it. A short, honest review is one of the most valuable things you can do.
How to protect yourself before it happens
Prevention comes down to layers. No single measure stops everything, but together they make you a harder, less appealing target. The most important layer is the one that makes ransomware survivable.
Back up properly, and test it
Reliable, tested backups are the single most effective defense against the damage ransomware causes, because they remove the attackers’ leverage. The key points:
- Follow the 3-2-1 rule: three copies of your data, on two types of storage, with one stored offsite.
- Keep at least one backup offline or immutable, so ransomware can’t reach it. A backup drive that stays plugged in is vulnerable.
- Use backups with version history, so you can go back to a point before the infection.
- Test restores regularly. An untested backup is a hope, not a plan.
- Remember that syncing services like cloud drives aren’t a replacement for backups, since encrypted files can sync and overwrite the good copies. Check how version recovery works on yours.
Keep everything updated
Turn on automatic updates for your operating system, browser, and applications. For routers, VPNs, firewalls, and servers, keep firmware current. Attackers quickly exploit known flaws, and a patch applied promptly closes the door.
Strengthen logins
Use long, unique passwords for every account, ideally stored in a password manager. Turn on two-factor authentication everywhere it’s offered, with priority for email, financial accounts, cloud storage, and any remote access. An authenticator app or hardware key is stronger than text messages.
Be careful with email and links
Slow down with unexpected attachments, urgent requests, and messages that push you to log in or pay quickly. Check the sender’s actual address. When in doubt, contact the person through another channel before opening anything. Disabling macros in Office documents from outside sources removes a common trick.
Limit what any one account can do
Use a standard user account for daily work rather than an administrator account. If malware runs under a limited account, it can do less damage. In organizations, give people access only to what they need for their jobs.
Lock down remote access
Don’t leave remote desktop services open to the internet. Put them behind a VPN with multi-factor authentication, or disable them if you don’t need them.
Use security software and keep it on
Reputable antivirus or endpoint protection software, with real-time protection switched on, can catch many known threats. Built-in tools in current versions of Windows and macOS are a reasonable baseline. For businesses, more advanced tools that monitor for suspicious behavior can detect an attack in progress.
Segment your network
In a business, separating systems so that one infected machine can’t reach everything limits the blast radius. Keep backups and critical servers on separate, more tightly controlled segments.
Train people
Employees, family members, and kids are common targets. Short, practical guidance on spotting phishing and reporting something suspicious without fear of blame makes a measurable difference. People who report a mistake quickly give you time to contain it.
Make a plan before you need one
A written incident response plan means nobody is improvising under stress. It should say who to call, how to isolate systems, where backups are, who handles communication, and which outside contacts (IT provider, insurer, lawyer, law enforcement) to reach. Keep a printed copy somewhere accessible, because if your systems are down, a plan stored on them is no use.
What small businesses should do specifically
Small businesses are often hit hard because they combine valuable data with thin defenses. If that’s you, a short priority list:
- Know what you have. List your critical systems and data, and where they live.
- Fix the basics. Updates, multi-factor authentication, and strong passwords across the board.
- Build proper backups. Include an offline or immutable copy, and test recovery, including how long a full restore would take.
- Consider cyber insurance. Read what it requires and covers, since some policies expect specific security controls.
- Know who you’d call. Have an IT or incident response contact identified before an incident.
- Review who can access what. Remove old accounts, limit administrator rights, and secure remote access.
None of this needs a huge budget, and it prevents most of the disasters that close businesses down.
What individuals and families should do
If you’re protecting a household rather than a company, the list is shorter:
- Keep one backup disconnected, and another copy offsite or in the cloud with version history.
- Turn on automatic updates on every device, including phones and tablets.
- Use a password manager and two-factor authentication.
- Avoid pirated software and unknown downloads.
- Be suspicious of unexpected email attachments and links.
- Talk to the whole family, including children, about not clicking unfamiliar links or running unknown programs.
Common myths about ransomware
“I’m too small to be a target.” Attackers often use automated methods and go for easy targets rather than specific ones. Being small doesn’t make you invisible.
“Antivirus will stop it.” Security software helps but isn’t foolproof. New variants appear constantly, and attackers deliberately try to bypass or disable protections.
“I have a backup, so I’m safe.” Only if the backup is intact, recent, unreachable by malware, and tested. Also, if data was stolen, backups don’t stop leaks.
“Paying fixes everything.” It frequently doesn’t, as covered above.
“It only happens on Windows.” Windows is a common target, but ransomware has been aimed at Macs, Linux servers, and other platforms too.
“If I turn the machine off, the problem goes away.” Powering off may stop encryption temporarily, but the infection is still there and evidence may be lost. Isolate first and seek guidance.
A quick action checklist
If you’re hit:
- Disconnect the affected device from all networks.
- Unplug backup drives and check your backups.
- Photograph the ransom note and preserve evidence.
- Don’t wipe or reinstall yet.
- Identify the strain and check for a free decryptor.
- Change passwords from a clean device and enable two-factor authentication.
- Report to law enforcement, and notify your insurer and IT support if you’re a business.
- Get legal advice before considering any payment.
- Rebuild systems and restore from clean backups.
- Patch the weakness that let attackers in, and monitor afterwards.
To prepare:
- Back up using the 3-2-1 rule, with one copy offline.
- Test your restores.
- Turn on automatic updates.
- Use unique passwords and two-factor authentication.
- Lock down remote access.
- Train yourself and others to spot phishing.
- Write down your response plan.
Frequently asked questions
What is ransomware in simple terms?
It’s malicious software that locks your files or device and demands payment to unlock them. Many modern attacks also steal your data and threaten to publish it.
How does ransomware spread?
Most often through phishing emails, stolen or weak passwords, exposed remote access, and unpatched software. Once inside a network, it can spread from machine to machine and onto connected drives and shares.
Can ransomware be removed without paying?
The malware itself can usually be removed by cleaning or rebuilding the system. Recovering the encrypted files without paying depends on having backups or on a free decryptor existing for that variant.
Can encrypted files be decrypted without the key?
Usually not, unless researchers have found a flaw in that specific ransomware or recovered its keys. That’s why checking resources like No More Ransom is worthwhile, and why backups matter so much.
Will paying the ransom get my files back?
Not reliably. Some victims never receive working decryption tools, and payment doesn’t guarantee stolen data is deleted. Authorities generally recommend against paying.
Does ransomware affect phones?
It can, though it’s less common than on computers. Android devices in particular have seen lockers and file-encrypting malware, usually from malicious apps installed outside official stores. Keep your phone updated and install apps only from official sources.
Does cloud storage protect me from ransomware?
Not by itself. Synced files can be encrypted and overwritten. Cloud services with good version history and file recovery help, but a separate, versioned, ideally offline backup is the safer approach.
How long does recovery take?
It varies enormously. A single home computer restored from backup might take hours. A business with many affected systems can take days or weeks to fully recover, which is why preparation and practice matter.
What should I do first if I see a ransom note?
Disconnect the device from the network, don’t pay or reply to the attackers, preserve the evidence, check your backups, and get help.
The bottom line
Ransomware is frightening because it turns your own data against you, but it’s also one of the more preventable kinds of attack. Most incidents begin with ordinary weaknesses: an unpatched system, a reused password, a convincing email. Most disasters are made worse by one thing, which is not having a recent backup you can actually restore.
If you’re hit, stay calm, isolate the machine, protect your backups, preserve evidence, and get help before making any decisions about payment. If you haven’t been hit, spend an hour this week on the basics: set up a backup with an offline copy, test a restore, turn on automatic updates, and enable two-factor authentication on your email. Those few steps change a ransomware attack from a catastrophe into an inconvenience.